Interacting with Apache Kafka Connect
The primary interface for interacting with Kafka Connect is the Kafka Connect REST API. To use it, you will need a TLS capable HTTP client such as curl or Postman.
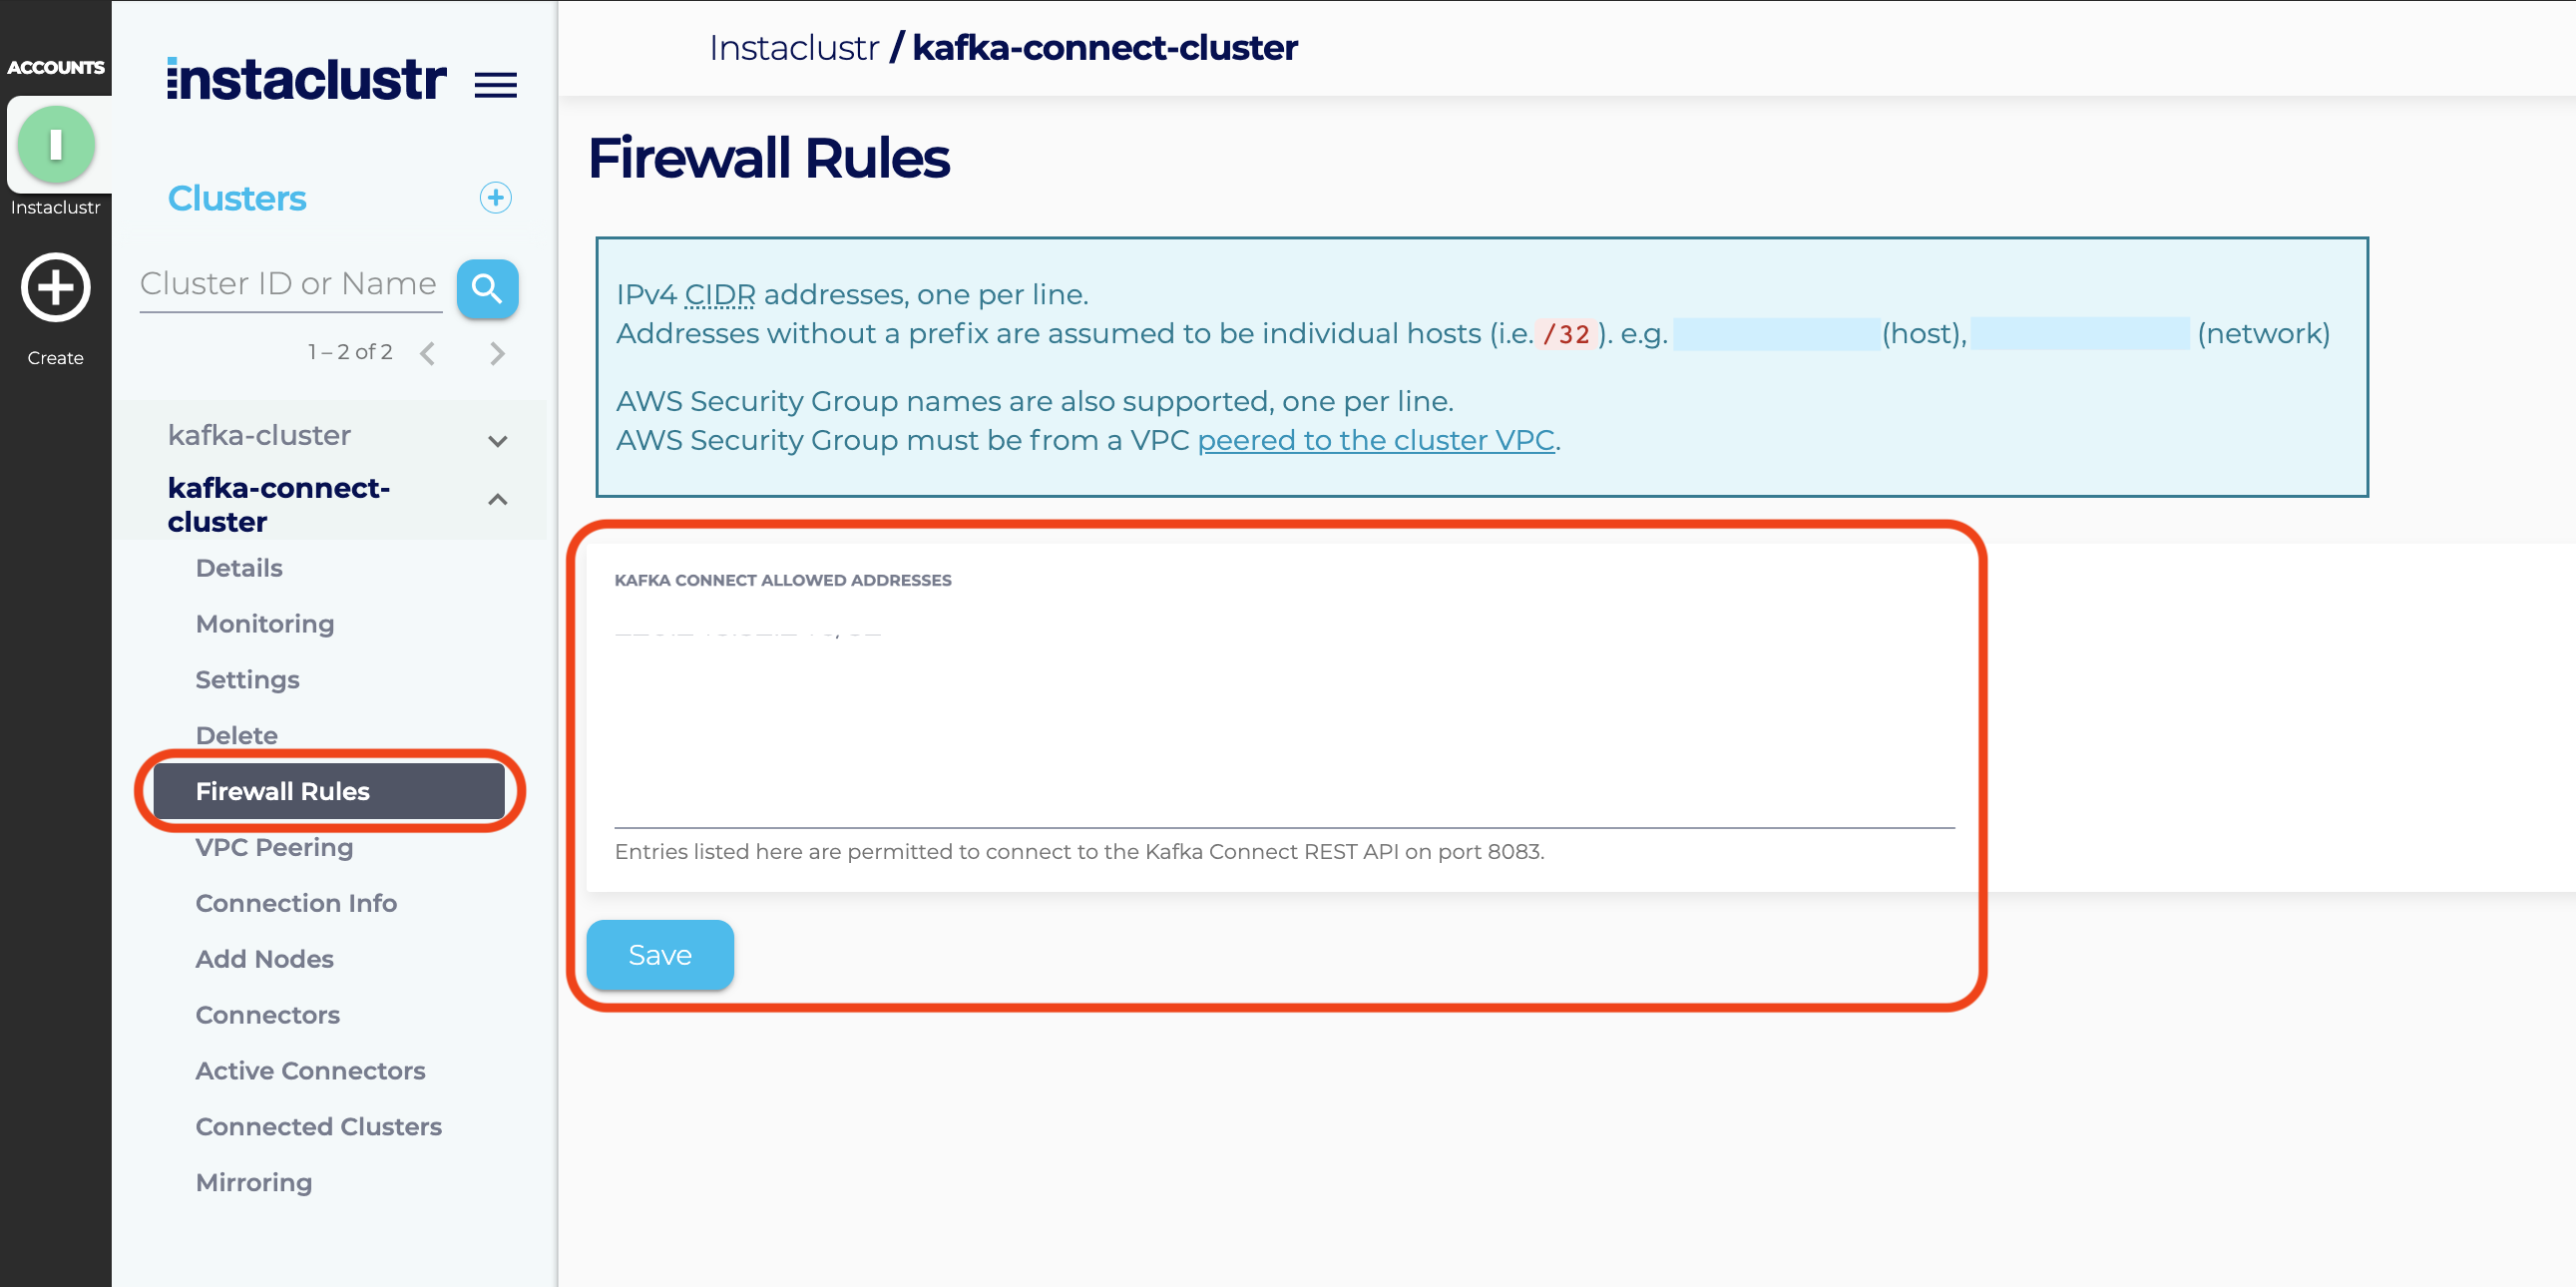
- First, you must ensure that your IP or IP range has been authorised to access the REST API. On your cluster’s Firewall Rules page, make sure there is an IP range that includes your IP. On AWS, you may instead authorise an AWS security group ID when clients connect through VPC peering. On AWS Bring Your Own Cloud (BYOC) clusters, you may also authorise a customer-managed prefix list ID (pl-…). Do not add an overly permissive CIDR, such as 0.0.0.0/0, and do not include one in a prefix list.
- All of the nodes in your cluster will be running a REST API that you can connect to. They all have equal functionality, so you can connect to any of them.
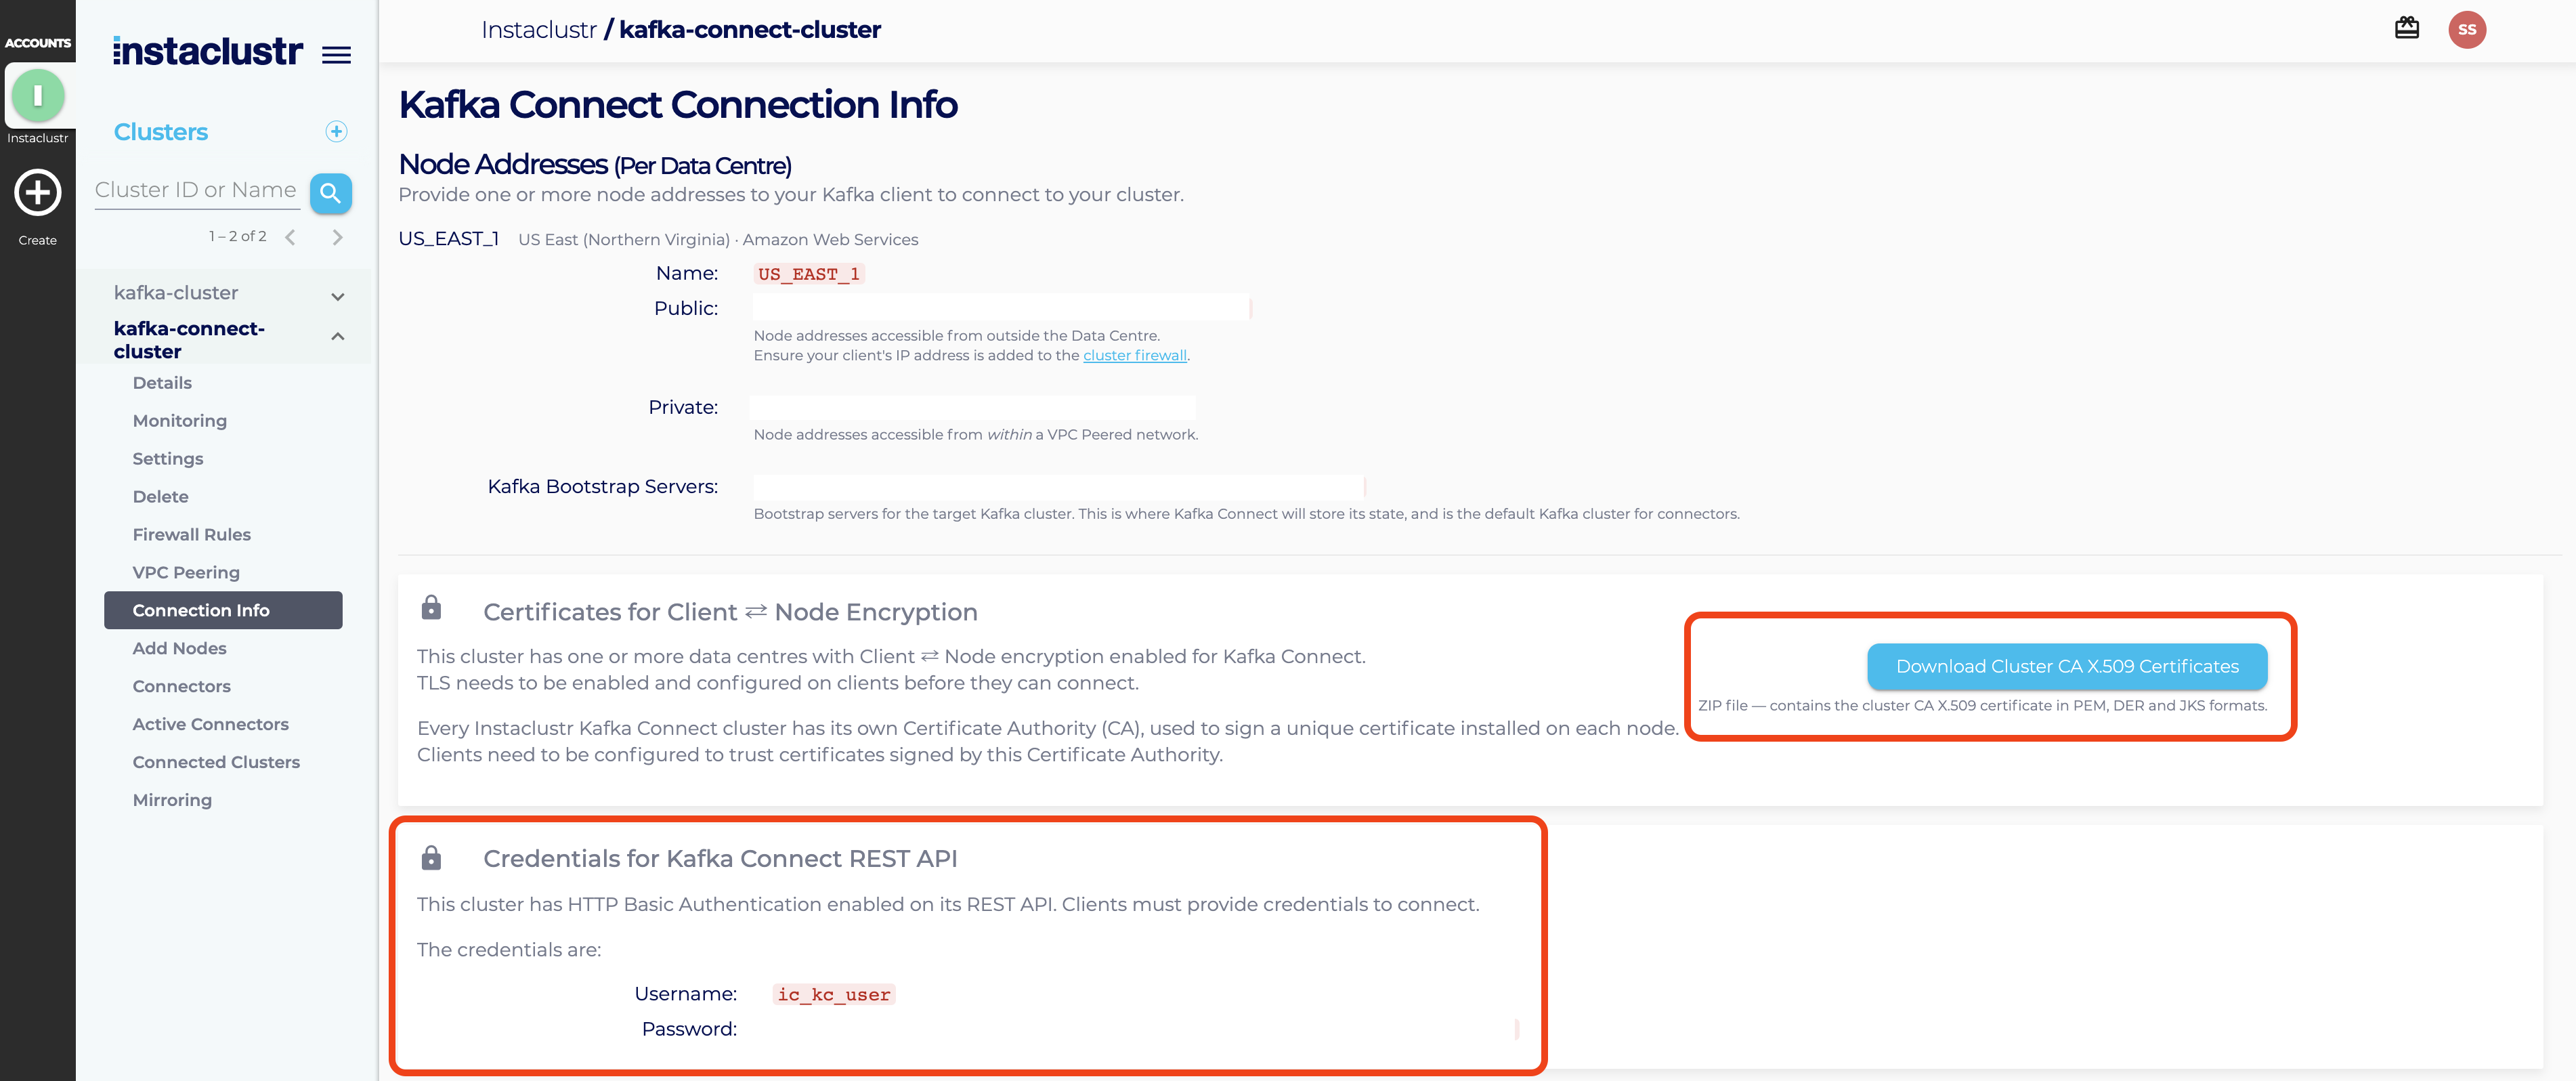
- You will need to obtain the access credentials for your REST API from the Connection Info page. If your HTTP client is configured to verify the server identity, you will also need to obtain your Kafka Connect cluster’s server certificates from the Connection Info page:
- With this information, you can now confirm your access to the REST API by issuing a simple request to show you which connectors are available in your cluster. NOTE: if Private Network add-on is enabled, you need to set up VPC peering before accessing the API, more information is at Connect to Kafka and Kafka Connect Using VPC Peering (AWS)
- As of 16 October 2026, newly provisioned Kafka Connect clusters support domain-based access. Connect to the Kafka Connect API using:
curl https://<url>:8083/connector-plugins --cacert <cert_path> -u <YOUR_USER>:<YOUR_PASSWORD>
Existing clusters will continue to use a node’s IP address:
curl https://<node_ip>:8083/connector-plugins --cacert <cert_path> -u <YOUR_USER>:<YOUR_PASSWORD>
Any customers wishing to migrate to using the domain-based access can ask for a migration by opening a support ticket.